
Online help
The web host accessible to all
Procédure
ModSecurity is the application firewall (WAF, “Web Application Firewall”) for your LWS Panel hosting plan: it blocks dangerous requests before they reach your site. It is enabled by default and we manage its rules. If a legitimate action on your site is denied with a 403 or 406 error, you can find the rule that blocked it, disable that rule alone, or turn off ModSecurity temporarily for testing, from the “Mod security” tool in the “Security” section.
The ModSecurity Web Application Firewall is used to protect your website from web-based intrusions. It secures the application layer before requests reach the hosted site: detection of inclusion attempts, anti-spam protection, detection of exploits (it allows version numbers used to be hidden on error pages returned by the web server), brute-force login attempts on WordPress, access to sensitive files, etc.
We manage the rules and update them regularly, including in response to new vulnerabilities. We strongly recommend leaving ModSecurity enabled. If it causes problems with your applications, however, you can disable the rule that is causing the issue, or the entire firewall.
Do not confuse it with the other protections in the “Security” section:
Log in to your web hosting admin area and, in the Security section, click Mod security. The page shows the firewall status, the Configure button (rules), and, for each domain and subdomain, the View history button.
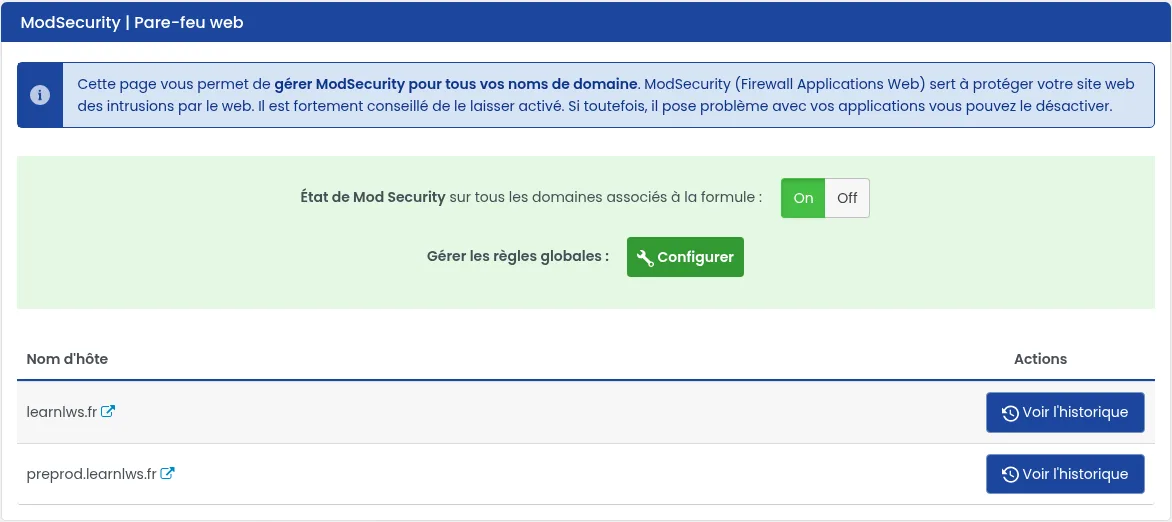
The Mod Security status on all domains associated with the plan switch (On / Off) enables or disables the firewall for all domains on your plan, including subdomains. Leave it set to On.
This may be the submission of a form, an action in your site’s administration area, or logging in to WordPress. Proceed in order and stop as soon as the action succeeds.
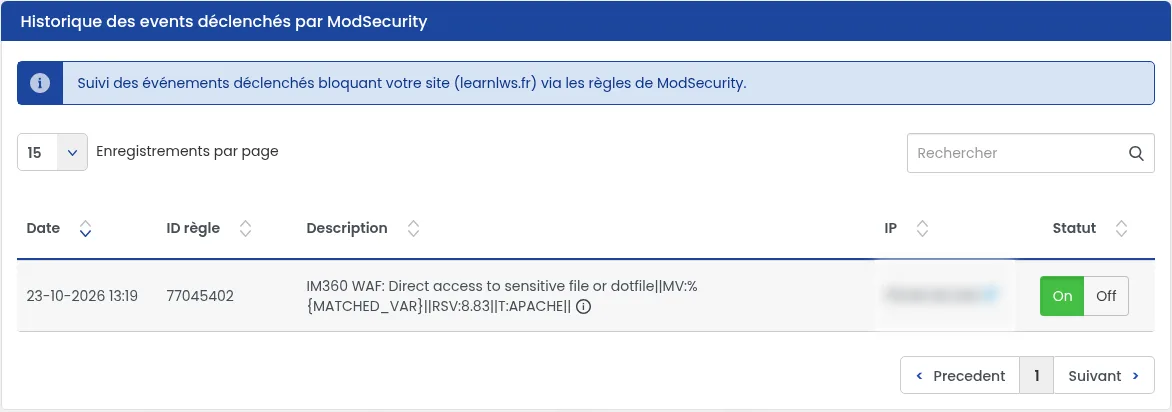
On the line for the relevant domain, click View history. Identify the event at the time of the block (the Search field accepts an IP address or a word from the description) and note its Rule ID and IP address.
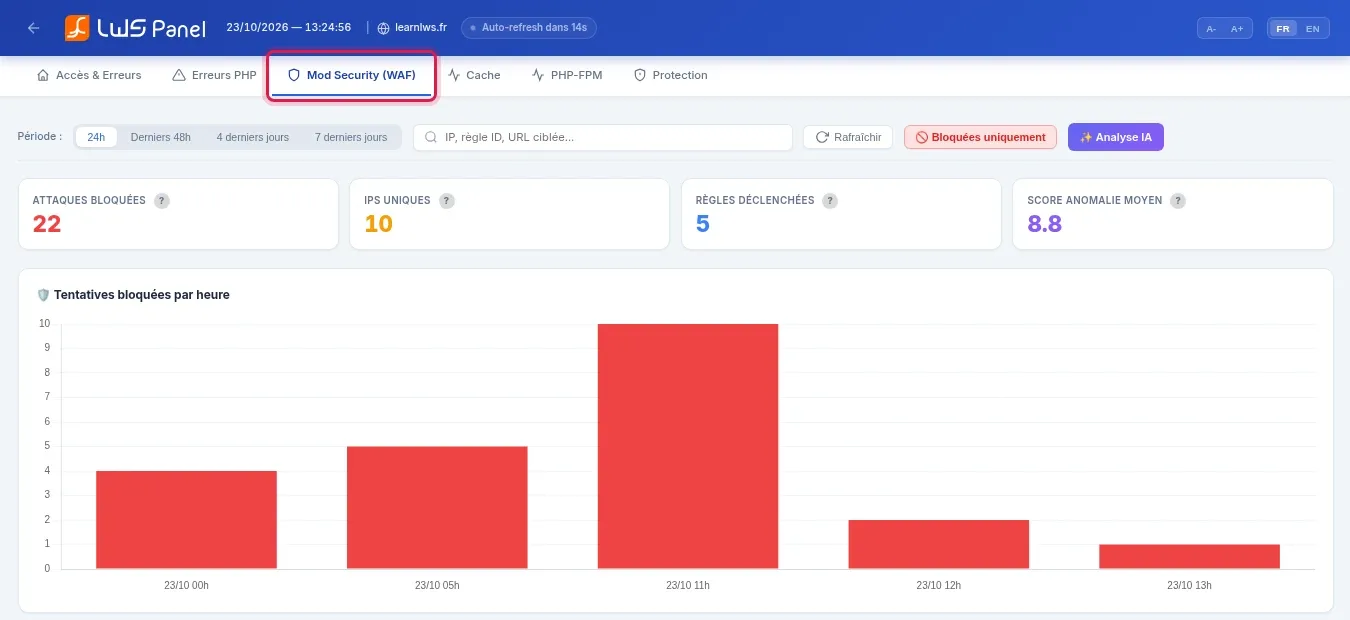
In the Databases & PHP section, click Apache PHP ModSecurity Logs, then open the Mod Security (WAF) tab. Enter the page address, your IP address or the rule number in the search field: the table shows, for each request, the date, IP address, method, URL, triggered rule and the “Blocked” status. The ✨ button next to a rule number explains the rule in simple language. The tool is presented in the help article How to access Apache / Php Logs.
Rather than turning off all of ModSecurity, set this rule to Off: either directly in the Status column of the history, or via Configure, by searching for the rule ID. The rule is disabled for your domain and the domains attached to it.
Switch the Mod Security status on all domains associated with the plan to Off, repeat the action, then switch it back to On.
Repeat the action that was blocked (form submission, saving, login) from the same internet connection.
The block comes from another protection. If a “Verification in progress” page appears, adjust the DDOS Firewall (Anubis) in the same “Security” section. If the error indicates 512 OL-BLACKLIST-IP, your IP address is blocked: follow the help article Error 512 - OL-BLACKLIST-IP. The Protection tab of LWS Log Analyzer also lists 509 and 512 blocks.
Look in the history for a “WordPress Bruteforce” rule and check the event’s IP address. If it is yours, also check in “Web IP Blacklist” that it is not blocked.
If the block persists, contact our technical support: How to contact technical support by email? Include with your request the exact page address, the action performed (form submission, saving, login, etc.), the exact date and time of the attempt with the time zone, the error code and full message or a screenshot, the rule number if it appears in the history, and your public IP address.
Ask the LWS team and the community. Answers are published after moderation.
 About LWS :
LWS is a 100% French web hosting company that focuses on quality and innovation and offers a responsive and competent technical service at affordable prices.


 Yes
 No